
Adobe Commerce now releases security patches every month, and Patching Automation (formerly CAPS) lets Cloud merchants apply them straight from the Admin. This page covers how the tool works, where it stops, and what it doesn't test, like your checkout, payments and integrations. It also shows how Evrig runs a safe monthly patching cycle around it, for Cloud, Open Source and Mage-OS stores.
Read MoreAdobe Commerce
3 Things to Lock In Before the Build Window Closes: Magento & Adobe Commerce 2026
Black Friday is Friday, November 27 and Cyber Monday is Monday, November 30. Before your build window closes, lock in caching and indexers, cron jobs and queues, and search and database performance on your Adobe Commerce or Magento store, and get security patches in ahead of code freeze.
Read More
Magento Checkout & Integration Testing Before Black Friday and Cyber Monday 2026
Test the whole journey before your code freeze: UX, payment failures, integrations, inventory sync and queues for Adobe Commerce and Magento stores.
Read More
The Adobe Commerce & Magento Black Friday and Cyber Monday 2026 Readiness Guide
A readiness guide for Adobe Commerce and Magento Open Source merchants preparing for Black Friday and Cyber Monday 2026 — covering UX, infrastructure, security, technical testing, promotions, monitoring, and post-sale review across a 5-phase timeline (Build → Harden → Lock → Live → Close), with the code freeze marked as the real deadline to work backward from.
Read More
Adobe Commerce Security Patch APSB26-92: What Magento Store Owners Need to Know
Learn what Adobe Commerce and Magento store owners need to know about APSB26-92, including affected versions, critical vulnerabilities, security updates, and safe patching practices.
Read More
Why an Unpatched Magento or Adobe Commerce Store Is an Open Door - and Why Patching Can't Be Occasional
An unpatched store is a known, actively targeted entry point for attackers — and the danger isn't only about running an old, end-of-life version. Plenty of stores on fully supported versions are exposed too, because a patch being available is not the same as a patch being applied. Keeping a store secure is an ongoing discipline: monitor for new vulnerabilities, test each patch against your specific store, and deploy it fast — every time, on a predictable cadence. This guide explains the risk, the gap that catches most merchants, and what reliable patching actually looks like.
Read More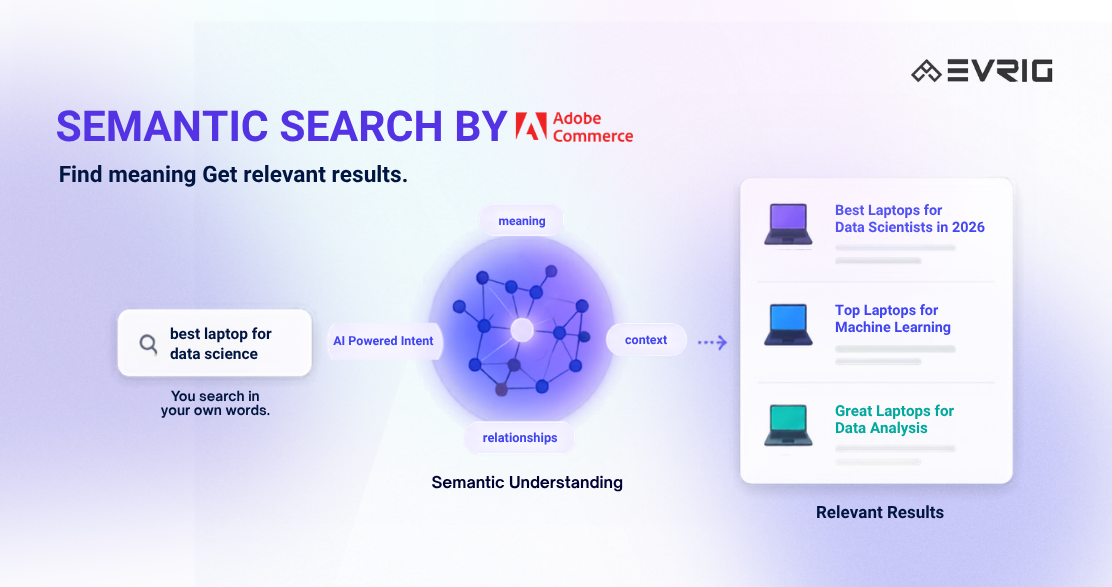
Semantic Search in Adobe Commerce: Help Shoppers Find the Right Products Faster
Discover how Semantic Search in Adobe Commerce Live Search uses AI to understand shopper intent, deliver more relevant search results, reduce zero-result searches, and improve conversions - all without requiring custom development or complex configuration.
Read More
APSB26-49 Security Patch Released for Adobe Commerce & Magento Open Source
Adobe has released APSB26-49, a critical security update for Adobe Commerce and Magento Open Source addressing multiple vulnerabilities, including arbitrary code execution, denial-of-service, and security feature bypass risks.
Read More
Magento / Adobe Commerce 2.4.6 Is Expiring: Upgrade Now Before Security & Revenue Are at Risk
Adobe Commerce 2.4.6 and earlier versions are nearing end of support and will no longer receive security updates. Upgrading to the latest version is essential to keep your store secure, stable, and fully supported. It’s a time-sensitive business risk.
Read More
Commerce & Magento Open Source Security Patch Released – Action Required
Adobe has released a new security patch for Adobe Commerce and Magento Open Source, addressing multiple vulnerabilities that could potentially impact the security of online stores if left unpatched. At Evrig, we strongly recommend that all merchants review and apply the latest security update as soon as possible to ensure their store remains protected.
You can review the official Adobe security bulletin here: APSB26-05